We don't just give you a checklist. We find the rules that apply to you and match them once. GCC rules come first, with international standards next to them. So one piece of proof answers many of them.
The rules that apply.
GCC rules first.
Do it once.
Use the proof everywhere.
How the matching works
Stop paying twice for the same work.
Many companies repeat the same work to follow the rules. This is because each set of rules is run as a separate project — PDPL and GDPR, ISO 45001 and ADNOC SSEMS. Each one is checked, proved and reported from the start. We find where they overlap and do that work once. Then one piece of proof answers many sets of rules.
01 · Matching the rules
Do it once, meet many rules.
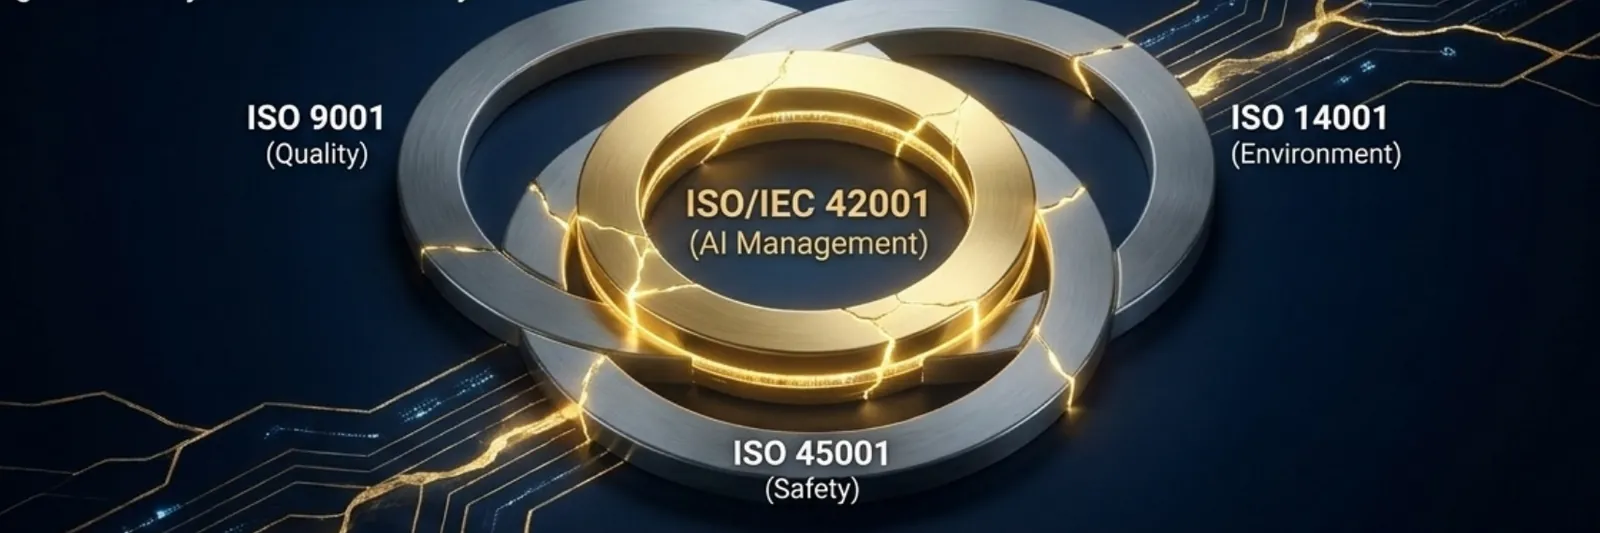
We find the requirements that are the same in PDPL, GDPR, ISO 42001 and ISO 27001. You do the work once and use the proof everywhere — instead of paying twice for the same thing.
02 · One set of proof
One document, many regulators.
We turn your raw material into documents that are ready for an audit. One document can answer several regulators and countries at once — not a separate file for each one.
03 · A clear position
Where you stand, one set of rules at a time.
For each set of rules that applies to you, we show what your proof already covers and what is still missing. So you know what to fix first.
GCC first.
International standards, linked to it.
What we cover
The rules that apply in the GCC.
What "covered" means here: a set of rules is covered when it is built into our assessment. It decides the proof we ask for and what goes in your report. It is not just a name on a list. These are the 29.
GCC laws & industry standards
— GCC first
ADNOC · CPS
ADNOC · ICV
ADNOC · AVL
ADNOC · HCMS
ADNOC · SSEMS
ADNOC · Marine
Aramco · CSMS
Aramco · HASP
Aramco · IMQ
Aramco · IKTVA
Aramco · OIMS
QatarEnergy HSE
OSHAD-SF
UAE TDRA
AI governance
UAE AI Charter
DIFC AI Regulation
EU AI Act (GCC exposure)
NIST AI RMF
OECD AI Principles
Data protection
UAE Federal PDPL
DIFC DP Law
ADGM DP Law
Dubai Data Law
Saudi NDMO
Qatar PDPL
Bahrain PDPL
GDPR (mapping)
International standards
— also covered, linked to the GCC rules above
ISO/IEC 42001
ISO/IEC 27001
ISO 31000
ISO 9001
ISO 14001
ISO 45001
ISO 19443 Nuclear
IEC 61511
SOC 2
We start with GCC rules because they are the ones that apply to you here. ISO and SOC are covered too. We link them to the GCC rules above, so the same proof works for both.
Which rules apply to you?
Tell us where you work and what you are getting ready for. We find the rules that apply to you and reply within two working days.
Prefer email? info@notjust4.ai